
Support Services
Technical support from the first design-in question to certification and long-term maintenance of your product.
Support Across the Entire Product Life
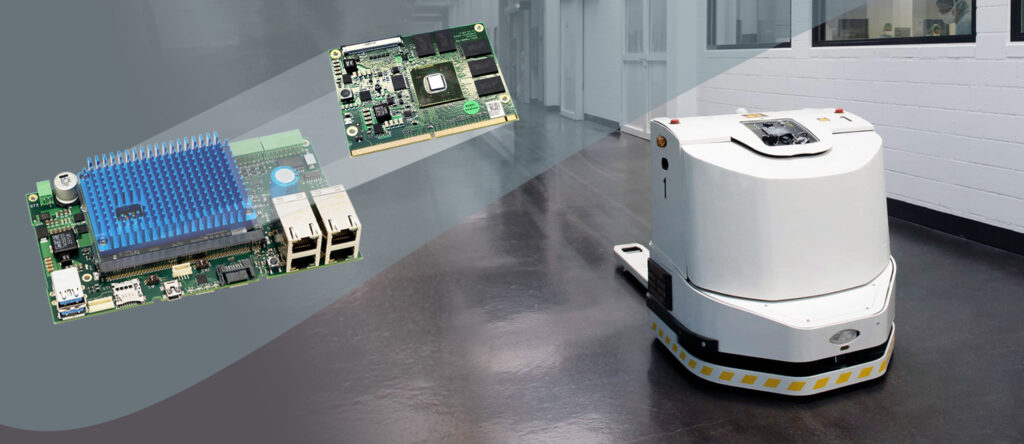
A product is only as dependable as the support behind it. MicroSys supports your team from the integration of our System-on-Modules into your hardware, through certification, to years of availability and security maintenance. The same engineers who develop our modules and software answer your questions.
Our support is organized in three areas: Design-In Support for the development phase, Certification Support for market access, and Product Lifecycle Management for the time after the start of production.
Design-In Support
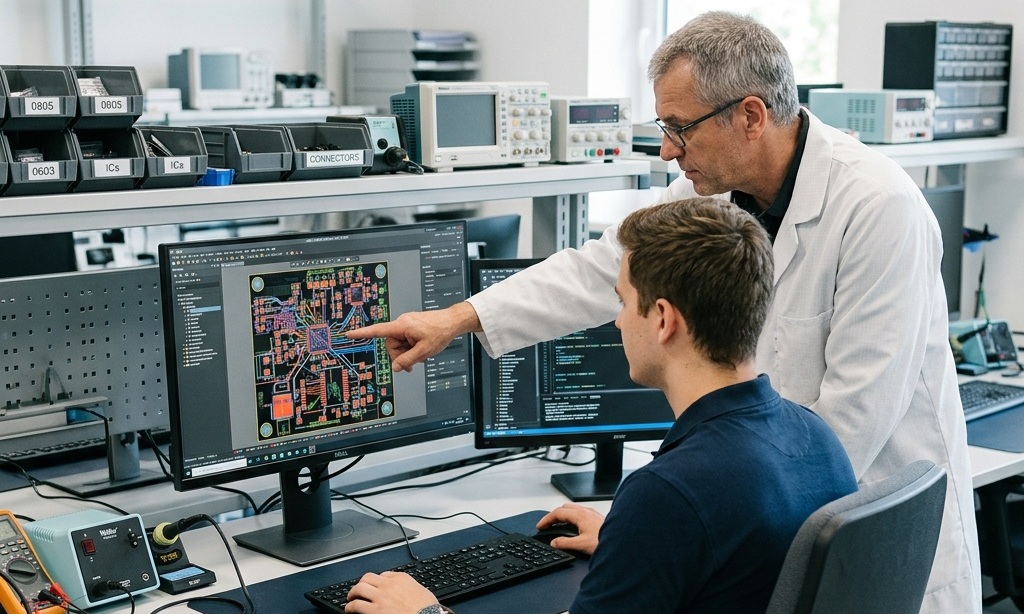
Integrating a System-on-Module into your own hardware is a critical phase of every project. Design-In Support gives your development team direct access to our hardware and software engineers, so that questions are answered before they turn into design changes. We tailor scope and effort to your project:
- E-mail support for quick answers to individual questions during evaluation and design
- Schematic review of the SoM connection and your mainboard
- Layout review, including placement, routing of critical interfaces and power and ground concept
- Access to our reference carrier design as a starting point for your own hardware
- Support with pin multiplexing and device tree configuration for your interfaces
- Board bring-up support, including power-up sequencing and first boot
- Access to development states via GitLab
- Priority handling of your requests
- A dedicated contact person for your project
If you would rather have us carry out the development, see our Hardware Development and Software Development services.
Certification Support
Products for industrial, vehicle, railway, avionics, medical or defense applications must meet domain-specific requirements before they can be placed on the market. We support you in all project phases on the way to the certification of your product, from requirements and design through verification to documentation. Certification takes place at product level; we provide the foundation, in the form of suitable hardware, documented processes and verification evidence.
Our support covers, among others:
- CE conformity
- EMC and overvoltage protection
- Shock and vibration
- Extended temperature ranges
- Environmental conditions such as salt water, dust and chemically aggressive media
- Functional safety for Industrial, Automotive, Avionics and Transportation environments
- Cybersecurity according to the Cyber Resilience Act (CRA)
We have realized projects in the regulatory environment of IEC 61508, DO-160 and EN 50155, and support development in the context of automotive functional safety (ISO 26262) and machinery safety in industrial automation (ISO 13849). Many of our System-on-Modules are prepared for use in these environments.
Our development follows a documented process based on the V-model, with requirements traced through to verification, and MicroSys is ISO 9001:2015 certified.
We support CRA compliance as part of our security engineering service.
Product Lifecycle Management
Our responsibility does not end with delivery. Product Lifecycle Management ensures that your product can be supplied reliably over many years and stays secure throughout its life. It covers three areas: longevity of supply, vulnerability management and incident management.
Longevity of supply
Embedded products may remain on the market for ten years or more. We select components and choose suppliers to meet or exceed these requirements.
Component EOLs are handled with speed and efficiency, and affected customers are informed through Product Change Notes (PCN).
Optionally, a frozen BOM is available: parts are pre-ordered and stocked so that we can continue to deliver even after component discontinuations.
Vulnerability management
Security remains part of the product life. For the scope of our products, we continuously monitor new vulnerabilities. Each finding is assessed and where action is required, we provide a security update. Affected customers receive the information they need to assess and mitigate the risk.
This gives your platform a well-integrated software foundation that connects hardware, processing cores and applications.
Incident management
Security incidents can be reported to info@microsys.de. We assess and classify each report, contain the incident, develop and verify a fix and inform affected customers. Actively exploited vulnerabilities are escalated immediately for regulatory assessment, in line with the CRA reporting obligations.
For customer-specific products, the security scope is defined in the product documentation and in the customer agreement.
Getting Started
Tell us about your project, and we will recommend the support type and level that fits.